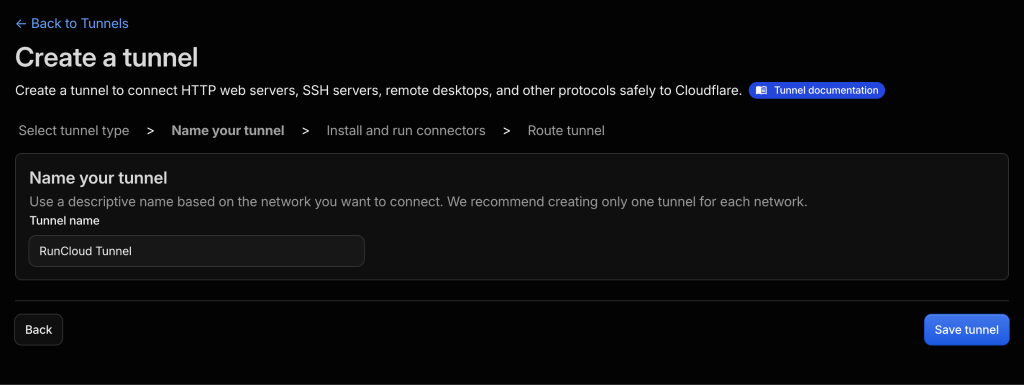
On the next screen, you need to provide a descriptive name for your tunnel. After entering the name, click “Save tunnel” to create a new tunnel.
Table of Contents
- 1 What is Cloudflare Tunnel?
- 2 Comparing Cloudflare Tunnel to a VPN
- 3 Step-by-Step Instructions for Configuring Cloudflare Tunnels
- 4 A Simpler Alternative: RunCloud Web Terminal
- 5 Wrapping Up
- 6 Frequently Asked Questions
- 6.1 Is Cloudflare Tunnel free?
- 6.2 Is Cloudflare Tunnel secure enough for production servers?
- 6.3 What is the difference between Cloudflare Tunnel and a VPN?
- 6.4 Can I tunnel SSH and a web app over the same cloudflared instance?
- 6.5 What happens to my tunneled services if Cloudflare has an outage?
- 6.6 Should I tunnel my database with Cloudflare Tunnel?
What is Cloudflare Tunnel?
When you set up a “Named Tunnel,” Cloudflare assigns it a unique ID (UUID) and creates a set of cryptographic credentials. Your cloudflared daemon uses these to stay connected. When a user tries to access your domain, Cloudflare routes that request through this secure, pre-established tunnel directly to your daemon, which then proxies it locally to your app or service.You might be wondering, “Why not just use a VPN?” While they both provide access, they serve different needs:
How the Daemon and Named Tunnels Work
If Cloudflare experiences an outage, your tunneled services will become temporarily unreachable from the public internet. However, your underlying server and applications remain safe and operational behind your firewall. Once Cloudflare restores its global network, the cloudflared daemon automatically reconnects your services without requiring a server reboot.It’s a fantastic way to maintain control while keeping your server’s SSH ports locked down.
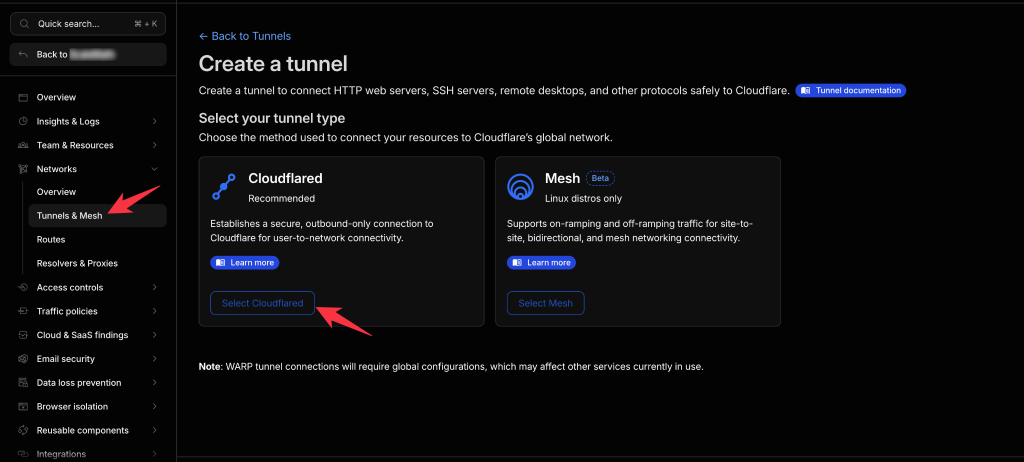
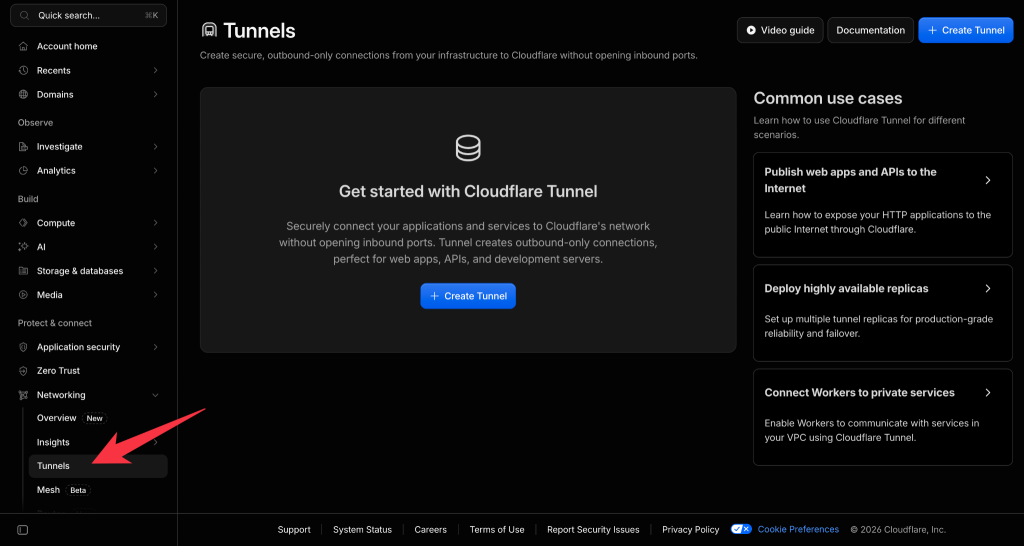
Alternatively, you can also access the same Cloudflare Tunnel menu by navigating to Networking > Tunnels.
Comparing Cloudflare Tunnel to a VPN
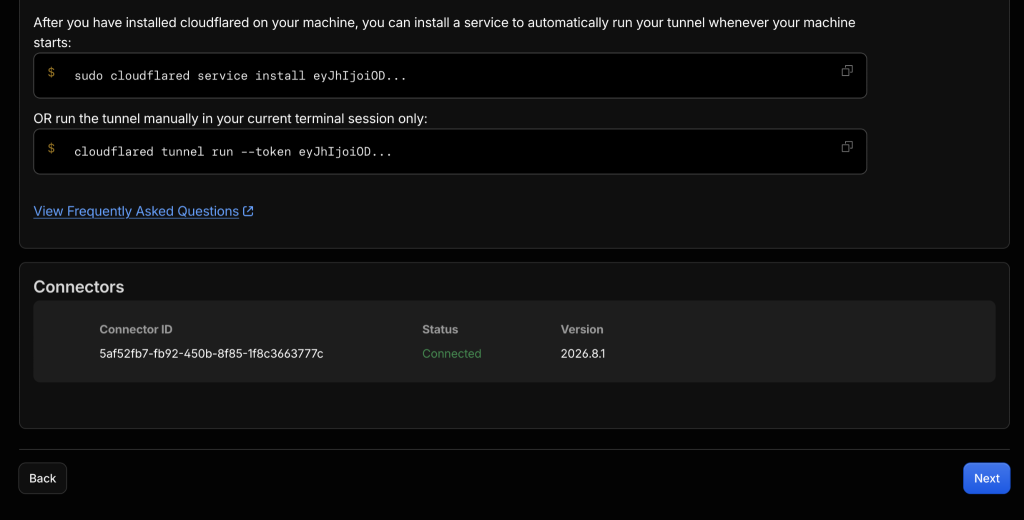
Once the tunnel is up and running, you will see your device listed in the Cloudflare dashboard. If you want, you can install the daemon on more devices using the same command, or scroll to the bottom and click Next to add routes.
- Cloudflare Tunnel works at the application layer (Layer 7). It’s perfect for exposing specific services, like a website or SSH, without giving someone keys to your whole network.
- Traditional VPNs work at the network layer (Layer 3). They directly connect your device to the remote network and grant access to every IP address and port on that subnet.
Before we talk about Cloudflare Tunnel, let’s first look at how we’ve traditionally handled server access. Usually, when you connect via SSH or access a web app, traffic flows from your device across the internet directly to your server’s public IP address. That requires your firewall to keep those “doors” (ports 80, 443, and 22) wide open.
Cloudflare Tunnel vs. VPN vs. Reverse Proxy
Suggested read: How to Use Cloudflare Firewall Rules to Protect Your Web Application
| Feature | Cloudflare Tunnel | Traditional VPN | Reverse Proxy (NGINX/Caddy) |
|---|---|---|---|
| Inbound Firewall Ports | None (0 ports open) | Requires 1 open port | Requires ports 80 & 443 open |
| Public IP Required? | No (works behind CGNAT) | Yes | Yes |
| Traffic Scope | Application-level (Layer 7) | Network-level (Layer 3) | Application-level (Layer 7) |
| Access Control Integration | Built-in Zero Trust / SSO | Requires external AAA/RADIUS | Requires manual auth modules |
| DDoS Protection | Included via Cloudflare | Requires third-party mitigation | Exposed to direct IP attacks |
Step-by-Step Instructions for Configuring Cloudflare Tunnels
This feature provides a collaborative, browser-based shell right in your RunCloud dashboard. It’s perfect for when you need to inspect logs, run a quick command, or collaborate with a teammate without opening ports or managing SSH keys locally.
Step 1: Getting Started with cloudflared
A traditional VPN grants users full network access to your entire infrastructure, which creates significant security risks if a device is compromised. In contrast, Cloudflare Tunnel safely exposes only specific applications without exposing your underlying network or server IP address. Cloudflare allows you to create Quick Tunnels for free without creating a Cloudflare account. This is useful for previewing and shipping ideas globally in seconds. However, in this section, we will build long-lasting, remotely managed tunnels, and the quickest way to do so is from the Cloudflare dashboard.
To prevent unauthorized users from accessing your server, you can secure it with Cloudflare Zero Trust. Whether you are protecting web applications, CLI connections, or SSH access, Cloudflare Zero Trust lets you gate access with identity controls.
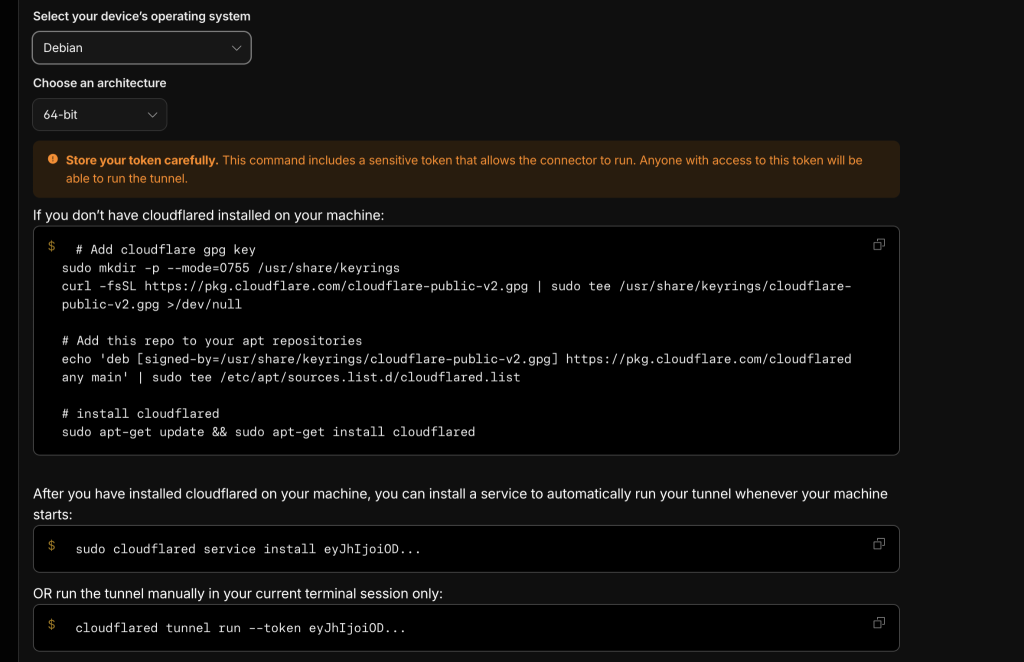
Copy and paste whichever command you wish to use. For this tutorial, we will only create a one-time tunnel.
While Cloudflare supports a wide range of authentication methods, this guide focuses on setting up a simple email-based One-Time Password (OTP) for quick setup.Now that your tunnel is running, you can securely expose your local applications to the internet directly from the Cloudflare dashboard without needing further CLI commands.
Authenticating the Daemon
In the past, securing a server meant taking on the headache of complex firewall rules, juggling SSH keys, or setting up jump hosts. But there’s a better way. Cloudflare Tunnel simplifies this approach by letting you expose your web applications, SSH access, and databases to the internet or only to authorized users, without opening a single inbound port on your firewall.
- Install a service to automatically run your tunnel whenever your machine starts.
- Run the tunnel manually only in your current terminal session.
Cloudflare Tunnel improves server security by eliminating the need to leave ports open. By routing your web apps, databases, and custom protocols through secure, outbound-only connections, you can unlock true Zero Trust protection against port scans and automated attacks.
Cloudflare Tunnel flips this dynamic entirely. Instead of your server listening for incoming connections, a lightweight background process, the cloudflared daemon, reaches out to Cloudflare’s edge data centers. Because the connection is strictly outbound, your server’s firewall can safely block all incoming traffic. You don’t even need a public IP address.
Suggested read: Cloudflare DNS for RunCloud (Security & Performance)
Step 2: Publish Application Route
However, when you pair this with RunCloud, managing a secure infrastructure becomes even simpler. RunCloud takes your server management to the next level with built-in features like the RunCloud Web Terminal. This feature comes configured out of the box, and there is no need to configure additional policies or install daemons, so it is quick and easy to access your command line securely without ever exposing SSH ports to the public internet.Log in to your Cloudflare account and open the Tunnel management page. You can access this from Zero Trust > Networks > Tunnels & Mesh > Cloudflared.
- Under the Hostname section, enter your desired subdomain (e.g., ‘localhost’) and select one of the domains connected to your Cloudflare account.
- Optionally, specify a path to route specific URL paths to this service, or just leave it blank.
- In the ‘Service’ section, select the protocol (e.g., HTTP) and enter the local address of your application. For example, if your app runs on ‘localhost:8765’, enter ‘localhost:8765’.
- After making the necessary changes, save the settings.
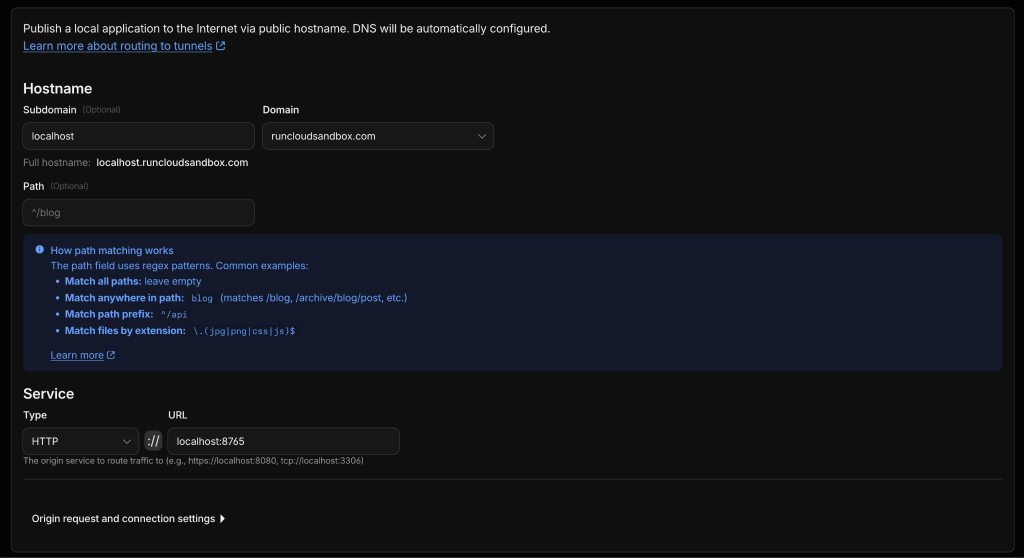
Yes, Cloudflare Tunnel is completely free to use as part of the Cloudflare Zero Trust platform. You can connect your server to Cloudflare without paying for extra bandwidth or connection limits. This makes it an affordable, enterprise-grade solution for securing your web applications and managing your servers.Now that we’ve covered the fundamentals and how Cloudflare Tunnel compares to traditional networking methods, let’s dive into setting it up. In the following section, we’ll walk you through the step-by-step process of installing and configuring Cloudflare Tunnel directly on your Linux server.To publish your application route:
Step 3: Secure Your Route with Cloudflare Zero Trust
Yes, a single cloudflared daemon instance can route multiple services simultaneously. You can configure your setup to direct web traffic to port 80 and SSH traffic to port 22 simultaneously. This setup lets you manage server access and web applications efficiently through one secure connection.Start your journey with RunCloud today.
- Navigate to Zero Trust > Access Control > Applications.
- Add a new Self-hosted application using the Public DNS template, then click Continue.
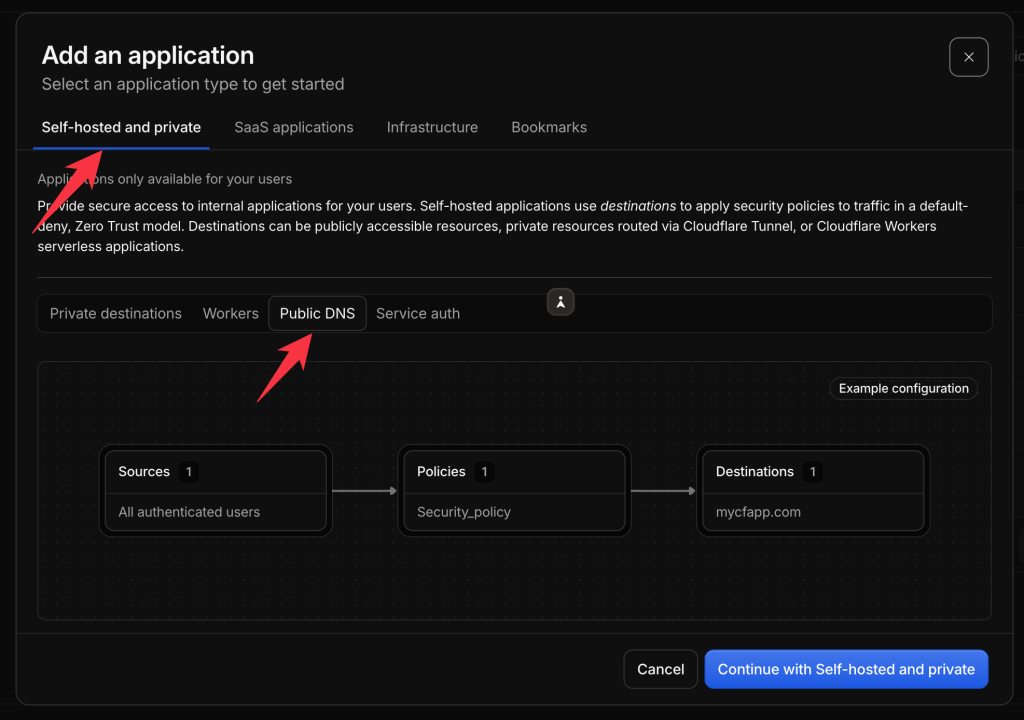
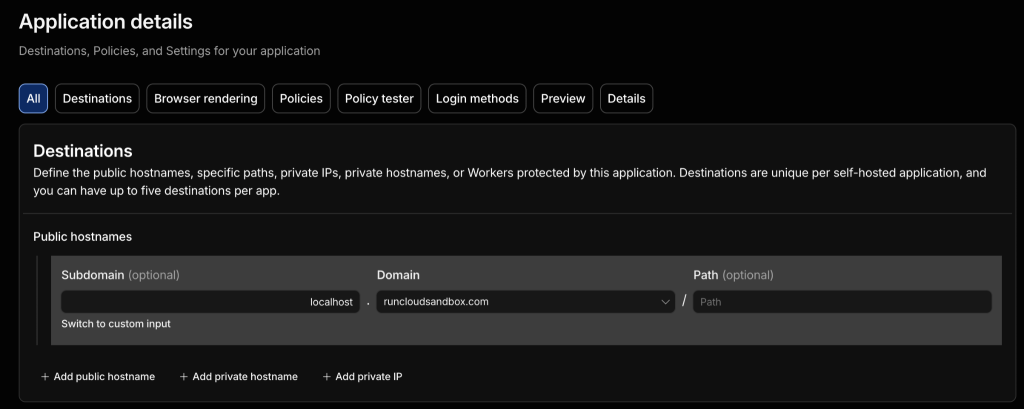
- On the next screen, under the Destinations section, set the subdomain, domain, and path settings to the same values that you configured in Step 2.
- Under the access policies section, create a new policy and create an access rule. You can create very complex rules as per your requirements. But to keep things simple, you can select “Email” from the dropdown and enter the list of email addresses that you want to allow access to.
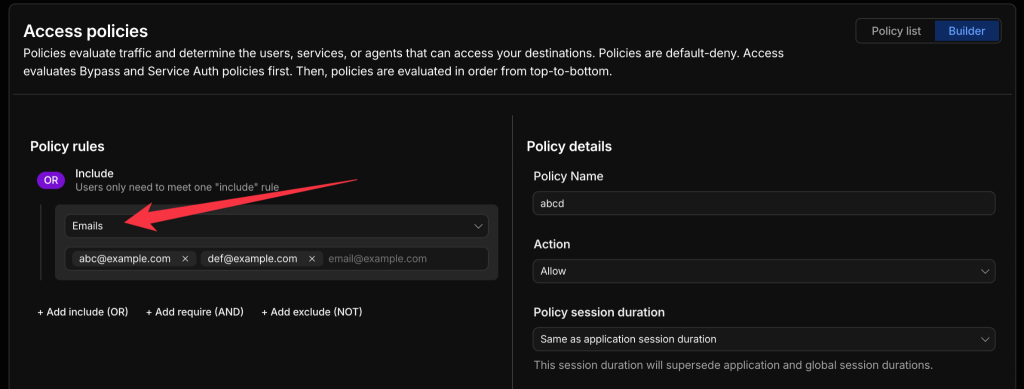
- After setting up your policy, you need to configure an identity provider. Scroll down to the Authentication section and under the “Choose available identity providers for this application” dropdown list, select “one-time pin”.
- After configuring your changes, save your settings. It usually takes a couple of minutes to take effect.
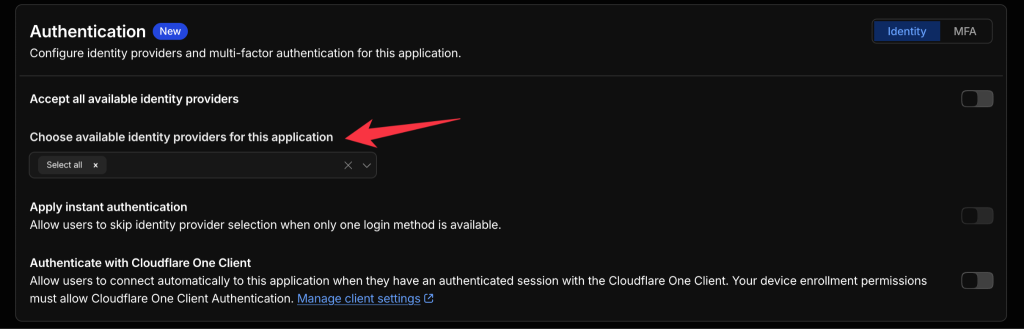
- After saving, anyone who tries to access your protected path will see this security prompt before they can access your application.
Suggested read: The 8 Best Cloudflare Alternatives in 2026
A Simpler Alternative: RunCloud Web Terminal
Exposing public ports on your server is a bit like leaving your front door wide open. If you’re managing Linux instances or running a web server, your systems are likely being pinged thousands of times a day by automated bots and scanners.The cloudflared daemon connects to Cloudflare using these credentials. When a user requests your domain, Cloudflare passes that request through the secure tunnel directly to cloudflared, which proxies it locally to localhost:80, localhost:22, or whichever internal port your app uses.
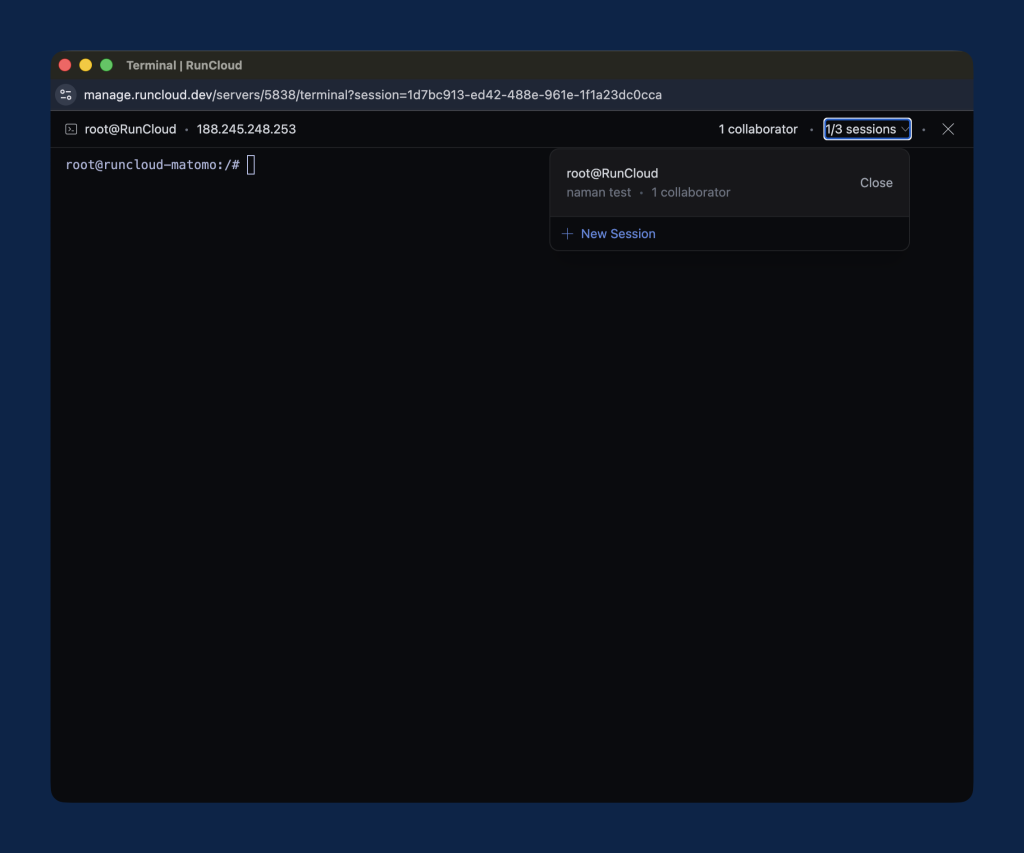
Why you’ll love the RunCloud Web Terminal:
- Zero Local Hassle: Access your shell from any device with a browser.
- No Key Management: Forget about distributing and rotating SSH keys; access is handled securely through RunCloud’s permissions.
- Enhanced Security: It’s off by default and requires 2FA, ensuring only you or those you authorize can access the shell.
- Real-Time Collaboration: You and your team can work in the same terminal window, making debugging a collaborative effort.
- Encrypted & Safe: Everything happens over an encrypted WebSocket connection via the RunCloud agent, keeping your secrets safe.
If you’re trying to figure out which tool fits your infrastructure, here’s a quick breakdown:
Wrapping Up
If you need full network-level routing, a dedicated VPN, or a mesh network like Tailscale is usually the better tool. But for securing individual apps or SSH access, Cloudflare Tunnel is hard to beat.Yes, Cloudflare Tunnel is built for production environments and uses outbound-only connections to prevent unauthorized access. By eliminating the need to open inbound public ports on your firewall, it protects your server from direct IP-based attacks and port scans. You also get automatic encryption and full integration with Cloudflare security and DDoS protection features.While Cloudflare Tunnel is excellent for many use cases, you might be looking for a more streamlined way to access your server’s shell without the overhead of local configurations. That’s where the RunCloud Web Terminal comes in.